

Loading
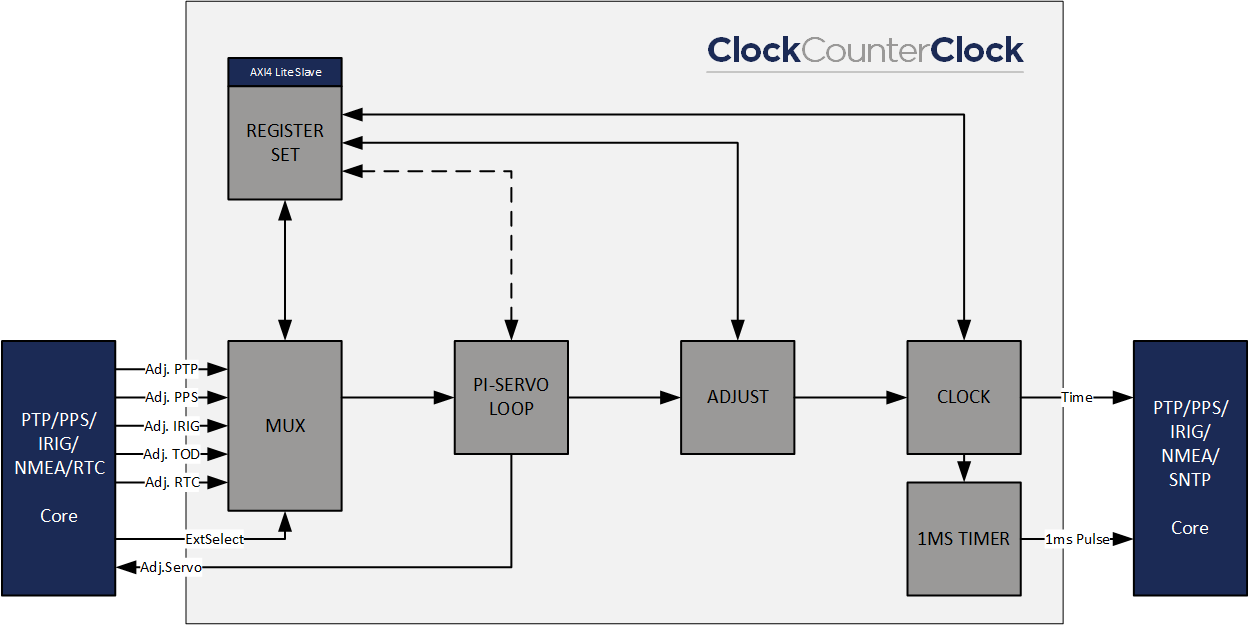
Adjustable Clock
Full standalone hardware only solution of an adjustable Counter Clock
By NetTimeLogic GmbH


Advanced Formal Verification
This is the advanced course of a two course formal verification progression. It assumes comprehensive knowledge of “Applied Formal Verification” and applies formal methods to the problems that dominate real Altera SoC designs.
By FPGA Authority
Advanced FPGA Design Methodologies and Techniques
This comprehensive course consolidates the full breadth of advanced FPGA design knowledge into a single intensive program.
By FPGA Authority
Advanced Platform Designer
This advanced course elevates engineers from solid Platform Designer users to expert-level practitioners.
By FPGA Authority
Advanced SoC System Design & Verification
This advanced course brings together all disciplines of Altera SoC FPGA design into a comprehensive system design and verification experience.
By FPGA Authority
Advanced Verilog Design Techniques
This course teaches designers to write professional, synthesizable RTL code using industry-standard Verilog HDL practices.
By FPGA Authority
Advanced VHDL
This advanced, hands-on course is designed for experienced FPGA engineers who want to deepen their mastery of VHDL.
By FPGA Authority
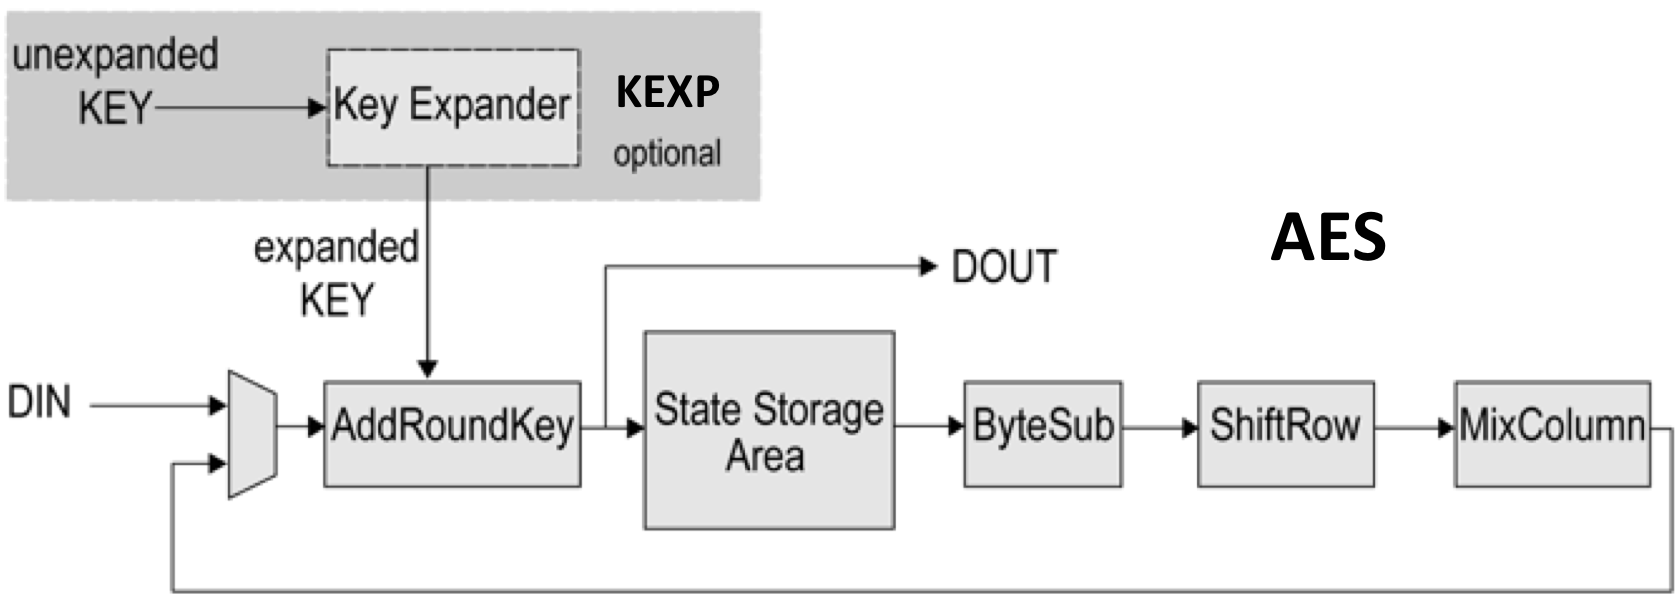
AES - Advanced Encryption Standard Engine
The AES encryption IP core implements hardware Rijndael encoding and decoding in compliance with the NIST Advanced Encryption Standard. It processes 128-bit blocks, and is programmable for 128-, 192-, and 256-bit key lengths. Two architectural versions are available to suit system requirements. The Standard version (AES-S) is more compact, using a 32-bit datapath and requiring 44/52/60 clock cycles for each data block (128/192/256-bit cipher key, respectively). The Fast version (AES-F) achieves higher throughput, using a 128-bit datapath and requiring 11/13/15 clock cycles for each data block. Various cipher modes can be supported (CBC, CFB, CTR, ECB, LRW, and OFB). The core works with a pre-expanded key, or with optional key expansion logic. The AES core is a fully synchronous design and has been evaluated in a variety of technologies. It is available optimized for ASICs or FPGAs, with complete deliverables.
By Computer Aided Software Technologies, Inc (dba CAST)

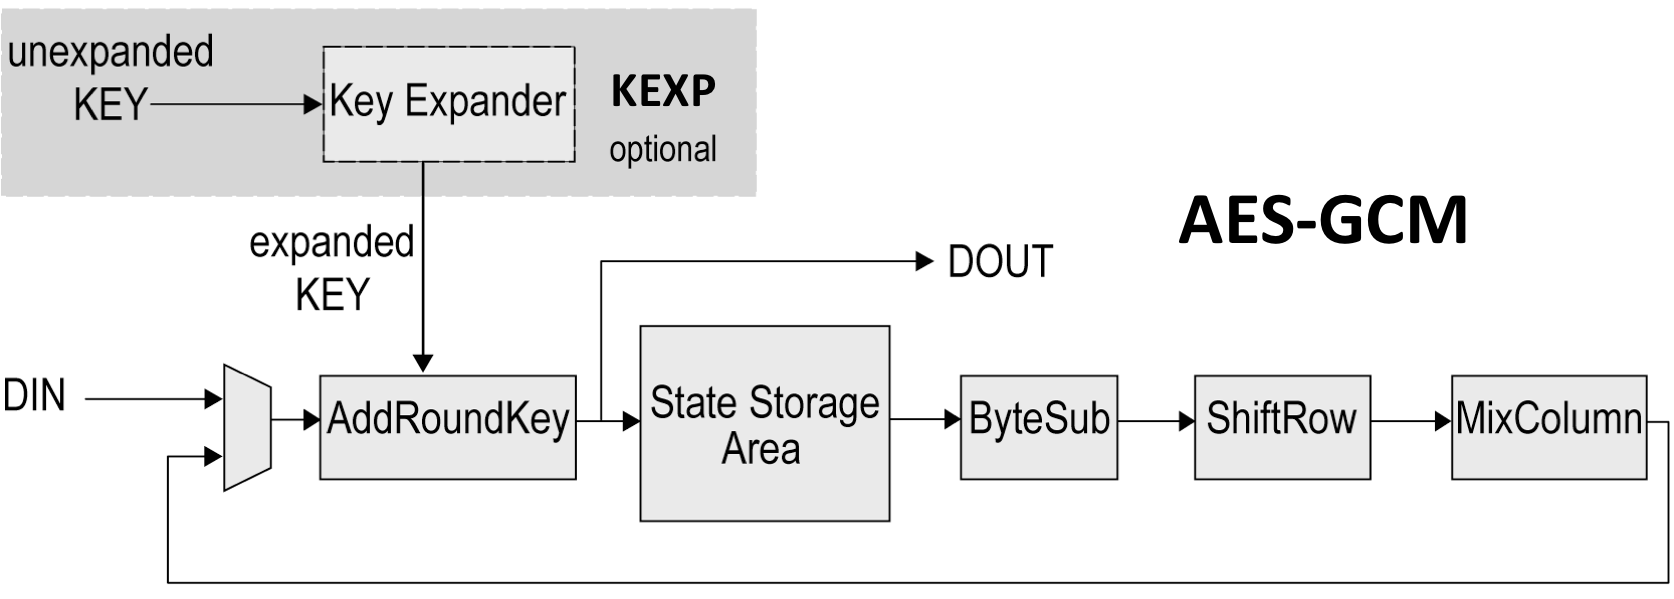
AES-GCM: Authenticated Encrypt/Decrypt Engine
The AES-GCM IP core implements NIST Advanced Encryption Standard (AES) in Galois Counter Mode (GCM). GCM is an authenticate-and-encrypt block cipher mode where a Galois Field (GF) multiplier/accumulator is utilized to generate an authentication tag while CTR (Counter) mode is used to encrypt. The core processes 128-bit blocks and is programmable for 128-, 192-, and 256-bit keys. Four architectural versions are available to suit system requirements. The Standard version (AES-GCM-S), more compact using a 32-bit datapath, requires 44/52/60 clocks for each data block (128/192/256-bit key, respectively). The Fast version (AES-GCM-F) achieves higher throughput using a 128-bit datapath and requires 11/13/15 clocks for each data block depending on key size. For high-throughput applications there are two additional versions. The High Throughput AES-GCM-X can process 128 bits/cycle and the Higher Throughput AES-GCM-X2 can process 256 bits/cycle respectively independent of the key size.
By Computer Aided Software Technologies, Inc (dba CAST)